

Introduction
Encryption protects sensitive information by converting readable data into an encrypted format.
Organizations use encryption to protect databases, cloud storage, applications, backups, communications, and other digital assets.
However, encryption depends on cryptographic keys.
A cryptographic key determines how information is encrypted, decrypted, signed, or authenticated. If an attacker obtains a sensitive key, the security of the information or service associated with that key may be affected.
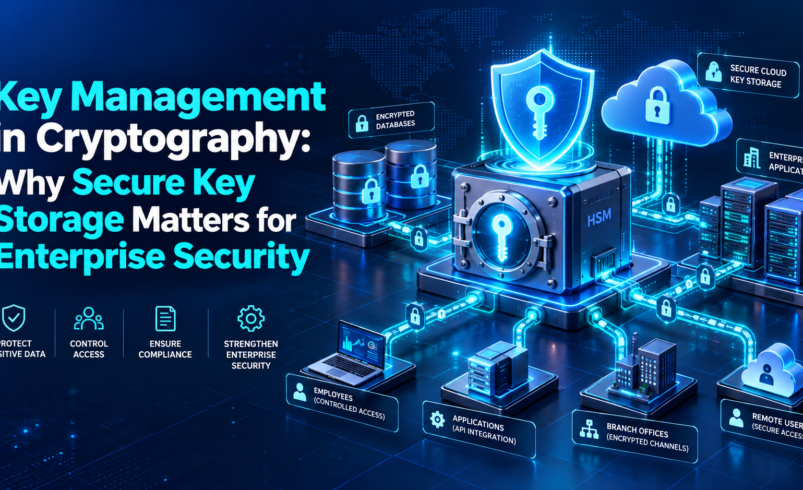
This makes secure key storage one of the most important components of enterprise cryptographic security.
Key management in cryptography provides the framework organizations use to protect keys throughout their lifecycle.
Effective Key management ensures that organizations do not simply store keys securely but also control access, usage, rotation, recovery, and retirement.
What Is Secure Key Storage?
Secure key storage means protecting cryptographic keys against unauthorized access, modification, disclosure, or loss.
Organizations should store sensitive keys in environments designed to provide appropriate security controls.
They should avoid storing keys in locations that unauthorized users or compromised applications can easily access.
Why Encryption Keys Are Sensitive
Encryption keys can control access to protected information.
Consider an organization that encrypts a database containing customer records.
The database may remain encrypted, but an authorized application still needs access to the corresponding cryptographic key.
If an attacker gains access to that key, the attacker may potentially undermine the protection provided by encryption.
This is why organizations must protect keys independently from the data they secure.
Key Management in Cryptography
Key management in cryptography covers the complete lifecycle of a cryptographic key.
The lifecycle typically includes:
- Generation
- Storage
- Distribution
- Access
- Usage
- Rotation
- Backup
- Recovery
- Retirement
- Destruction
Secure storage represents only one part of this lifecycle.
Organizations should implement controls at every stage.
Risks of Poor Key Storage
Poor key storage practices can create several risks.
Keys in Source Code
Developers may accidentally expose cryptographic keys by placing them directly into application source code.
Keys in Configuration Files
Unprotected configuration files can expose sensitive keys.
Keys Alongside Encrypted Data
Storing keys alongside encrypted information can reduce the effectiveness of encryption if attackers compromise the storage environment.
Excessive Access
Too many users or applications may gain access to sensitive keys.
Unencrypted Backups
Poorly protected key backups can create additional exposure.
Separating Keys From Data
Organizations should maintain appropriate separation between cryptographic keys and the data they protect.
For example:
Encrypted database → Protected database environment
Encryption key → Dedicated key management infrastructure
This separation creates an additional security boundary.
Access Control
Secure key storage must include strong access controls.
Organizations should apply least privilege.
Only authorized users and applications should access specific cryptographic keys.
Security teams should define:
- User permissions
- Application permissions
- Administrative roles
- Authentication requirements
- Key-specific access
Authentication for Key Administration
Administrative access to key management systems should receive strong protection.
Organizations should use appropriate authentication and authorization mechanisms.
Administrative activity should also receive monitoring and logging.
Key Rotation
Secure storage does not eliminate the need for key rotation.
Organizations should establish policies for replacing cryptographic keys.
Rotation schedules may depend on:
- Key age
- Data sensitivity
- Security requirements
- Regulatory obligations
- Risk assessments
Organizations should test rotation procedures before applying them to critical systems.
Key Backup
Organizations need backups for critical cryptographic keys.
However, backups require the same level of security attention as active keys.
Security teams should protect backup locations and restrict recovery permissions.
Key Recovery
Key recovery procedures should be documented.
Organizations should determine:
- Who can recover keys
- Under what circumstances recovery is allowed
- Where backups reside
- How recovery is authorized
- How recovery activity is monitored
Businesses should test recovery procedures regularly.
Hardware-Based Protection
Some organizations may use dedicated hardware security technologies to provide stronger protection for high-value cryptographic keys.
Hardware-based controls can help isolate sensitive cryptographic operations from general-purpose application environments.
Organizations should select technologies according to their security requirements and architecture.
Monitoring Key Storage
Security teams should monitor activities related to sensitive keys.
Important events include:
- Key access
- Key creation
- Key modification
- Key rotation
- Administrative changes
- Failed access attempts
- Key retirement
Monitoring can help identify unexpected activity.
Key Management and Cloud Environments
Cloud infrastructure introduces additional key storage considerations.
Organizations may operate across multiple cloud providers and on-premises infrastructure.
Security teams should understand where keys reside and which services can access them.
Centralized Key management can help organizations maintain consistent policies.
Key Management and Databases
Databases frequently contain sensitive business information.
Organizations use database encryption to protect this information.
However, encryption keys require separate protection.
Key management can provide structured controls around these keys.
Key Management and Digital Certificates
Digital certificates use cryptographic keys to establish trusted identities and secure communications.
Organizations should protect private keys carefully.
Certificate-related keys should also follow lifecycle processes such as monitoring, renewal, rotation, and retirement.
Common Key Storage Challenges
Lack of Inventory
Organizations may not know where every key resides.
Weak Access Controls
Too many users may have key access.
Poor Backup Protection
Key backups may not receive adequate security.
Manual Processes
Manual key administration can create errors.
Legacy Systems
Older applications may store keys in insecure ways.
Best Practices for Secure Key Storage
Organizations should:
- Maintain an accurate key inventory
- Separate keys from protected data
- Apply least privilege
- Protect administrative access
- Use appropriate secure key storage infrastructure
- Establish rotation policies
- Protect key backups
- Test recovery procedures
- Monitor key activity
- Retire obsolete keys
Conclusion
Secure key storage forms an essential part of enterprise cryptographic security.
Encryption protects sensitive information, but cryptographic keys control access to that protection.
Key management in cryptography provides the lifecycle framework required to generate, store, access, rotate, recover, and retire cryptographic keys.
Effective Key management reduces unnecessary key exposure and helps organizations maintain stronger control over encryption infrastructure.
By combining secure storage, least-privilege access, key separation, rotation, backup protection, monitoring, and recovery procedures, enterprises can build a more resilient cryptographic security framework.